Key events and trends
● Datadog's State of DevSecOps 2026 Report Highlights Supply Chain Vulnerabilities A report from Datadog on the state of DevSecOps in 2026 indicates that 87% of organizations possess at least one exploitable vulnerability. The median delay for library updates is 278 days behind the newest major version, and only 18% of critical vulnerabilities retain their high severity after refining their base CVSS scores. Furthermore, 32% of organizations utilized public Docker images within one day of a new version's release, with similar trends for JS and Python (55%). The report emphasizes the significant and growing threat of supply chain attacks. (источник)
● Major Updates Across Cloud Native Ecosystem Enhance Security and Monitoring Capabilities A digest of Cloud Native ecosystem updates includes several key releases:
- Argo Workflows 4.1 introduced 31 new features, including OpenTelemetry traces for the controller and executor, Kubernetes DRA support, Pod-level requests and limits, and database authentication via AWS RDS IAM and Azure PostgreSQL Entra ID. (источник)
- Prometheus 3.14.0 enabled PromQL duration expressions by default, promoted
first_over_timeto stable, added Oracle Cloud Infrastructure compute service discovery, and experimental support for encoding start timestamps in histograms. (источник) - Crossplane 2.4.0 improved resource watching, introduced zero replicas for safe-start provider runtimes until active, added vulnerability-scannable container images, and enhanced hardening across composition and package paths. (источник)
- Strimzi 1.2.0 gained Apache Kafka 4.3.1 support, templated (per Pod) additional volumes, eliminated auto-mounting of Service Account tokens into Pods, and saw server-side apply reach GA. (источник)
- Open Policy Agent (OPA) v1.20.0 introduced new Rego keywords (
andandor) for combining conditions within rule bodies. (источник) - Istio 1.31.0 added a GatewayClass for deploying agentgateway as a waypoint proxy, implemented the Gateway API AllowInsecureFallback feature for client certificate validation, included weighted waypoint canaries, zone-aware load balancing, mesh-wide default traffic policy, FIPS 140-3 compliance policy, and multi-target Prometheus scraping. (источник)
- Inspektor Gadget v0.56.0 introduced experimental support for Kubernetes multi-tenancy (based on namespaces), rootless
ig imagecommands, and switched to kubelet's/configzfor container runtime socket auto-detection. (источник)
● MCP-Server-Kubernetes Provides Secure Kubernetes Management Layer
mcp-server-kubernetes now exposes a complete Kubernetes management layer through the Model Context Protocol (MCP), allowing tools like Claude Desktop and mcp-chat to execute kubectl and Helm commands securely. (источник)
● New Kubernetes Operator Manages Resource Overcommit on Pod Requests
The k8s-overcommit-operator by InditexTech is a new Kubernetes operator designed to intelligently manage resource overcommit on pod resource requests, reclaiming idle capacity based on priority classes. (источник, источник)
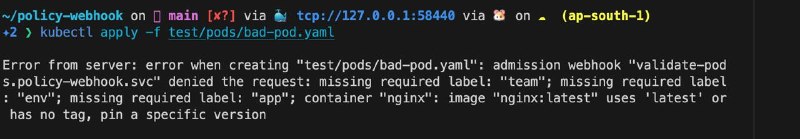
● Guide Released for Building a Kubernetes Admission Webhook in Go
An article was published detailing the process of building a Kubernetes admission webhook in Go from scratch, covering the TLS trust setup and addressing bootstrapping deadlocks. (источник)
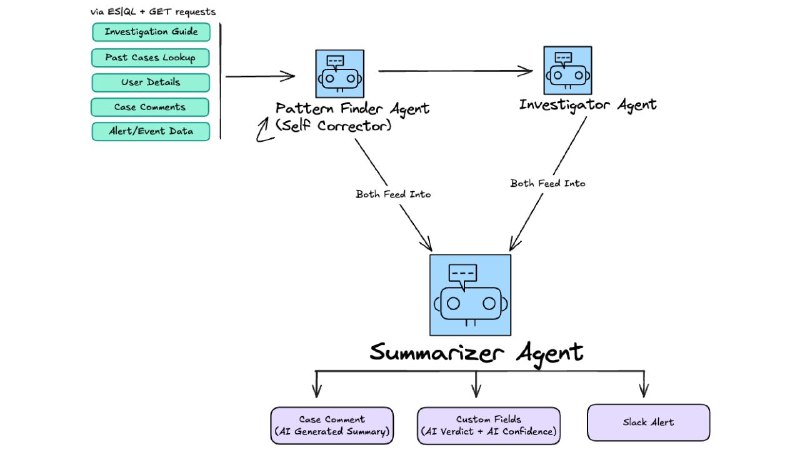
● Elastic Improves SOC Alert Triage Accuracy with AI to 92%
Elastic's InfoSec team reported an increase in AI alert accuracy from 60% to 92% within their three-agent SOC triage pipeline. This improvement was achieved by enriching the pipeline with per-rule investigation guides, user risk data, and 30 days of historical case verdicts, enabling analysts to resolve most alerts with a single click. (источник)
● Article Explores Distributed Database Coordination Failures An article titled "Why Distributed Databases Fail at Coordination Boundaries" offers insights into critical areas that require attention when working with any distributed system, particularly where independent components exchange timing, ownership, and state information. (источник)
Live discussions
No relevant live discussions were observed in the monitored groups for this period.
Social graph
No identified participants for the day due to the absence of discussions.
Final analytics
The activity for 16.09.2026 in the Kubernetes & DevOps domain was heavily focused on channel-driven announcements and reports, indicating a day of significant product evolution and industry insights rather than active community discourse. Key themes include the ongoing maturation of the Cloud Native ecosystem, with numerous updates to critical projects like Argo Workflows, Prometheus, Crossplane, Istio, and OPA, many of which directly address infrastructure security, policy enforcement, and monitoring capabilities.
A dominant concern highlighted by Datadog's "State of DevSecOps 2026" report is the prevalence of exploitable vulnerabilities and the persistent challenge of software supply chain security, particularly concerning delayed library updates and the rapid adoption of new Docker images. This underscores a continued industry-wide struggle to maintain robust security postures in fast-paced development environments. Innovations like the MCP-server-kubernetes for secure kubectl/Helm operations and the k8s-overcommit-operator for resource management reflect efforts to enhance both security and operational efficiency within Kubernetes environments. The lack of direct community discussions suggests that the information presented was primarily for consumption, or that any active dialogues took place outside the monitored channels.