Key events and trends
● Kubernetes Security: What Changes and What Stays in a Cloud-Native Environment Rodrigo Bersa from AWS outlined how moving to Kubernetes necessitates an additional layer of security, rather than replacing existing practices. Fundamental security concepts such as least privilege, perimeter security, network access control, authentication, and authorization remain essential. However, significant changes are required for supply chain security (due to the management of numerous container images), multi-tenancy (which is default and requires robust namespace isolation and network policies), and distinct in-cluster authentication models separate from infrastructure-layer controls. (источник)
● Case Study: Running ServiceNow MID Server on EKS with IRSA Credentials A team successfully implemented ServiceNow's MID Server on Amazon EKS using a StatefulSet. This setup involved faking the EC2 metadata service to allow the agent to accept IRSA (IAM Roles for Service Accounts) credentials, demonstrating a practical approach to secure identity and access management for enterprise applications within Kubernetes. (источник)
● Wiz Releases Security Best Practices for Claude Code Wiz published a detailed 7-page document outlining security best practices for leveraging Claude Code, an AI agent. This cheat sheet covers crucial aspects including Prompt Hygiene and Data Handling, Secure Code Generation with recommendations for safer output, Supply Chain Attack mitigation (e.g., checks for slopsquatting and lockfile management), and Access Control to limit agent capabilities and sensitive data access. Each section provides concrete action items and examples, concluding with advice on agent interaction, MCPs, and integrating security checks into CI/CD pipelines. (источник)
● ASCII Smuggling Exploited for Phishing Evasion
Microsoft researchers have identified a high-volume phishing campaign that utilizes ASCII smuggling, a technique previously associated with AI prompt injection, to evade email filters. This method involves splitting keywords, such as "funding," to bypass detection. At its peak in February 2026, the campaign generated over 2.3 million messages daily, underscoring ongoing challenges in information security and the sophistication of phishing tactics. (источник)
● New CLI Tool Kor for Unused Kubernetes Resource Cleanup
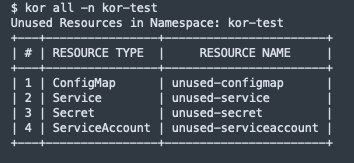
A new CLI tool named Kor has been introduced, designed to scan Kubernetes clusters and identify unused resources. Kor helps in the cleanup of forgotten ConfigMaps, Secrets, stale Services, and PVCs, addressing common operational challenges related to resource management and cost optimization in Kubernetes environments. (источник)
● dotenv-diff: A Tool for Validating Environment Variable Usage The GitHub project dotenv-diff offers a tool to validate environment variable usage within a codebase. This can be critical for ensuring applications deployed in server infrastructure are securely and correctly configured, thereby preventing potential vulnerabilities arising from misconfigurations. (источник)
Live discussions
No significant live discussions directly related to server infrastructure and its security were identified from the source data for this period.
Social graph
No identifiable participants with specific roles emerged from discussions in the source data for this period.
Final analytics
The day's information highlights a strong emphasis on bolstering security within cloud-native and DevOps ecosystems. Recurring themes include the dynamic nature of Kubernetes security, particularly concerning multi-tenancy and supply chain integrity, as evidenced by AWS insights and the ServiceNow EKS case study. The introduction of specific security best practices for AI-driven code generation, illustrated by the Wiz document for Claude Code, signifies the deepening integration of AI into DevSecOps and AppSec practices. Persistent threats, such as phishing campaigns employing advanced techniques like ASCII smuggling, reinforce the critical need for continuous vigilance and robust information security defenses. Furthermore, tools like Kor for Kubernetes resource management and dotenv-diff for environment variable validation underscore a growing focus on operational hygiene and secure configuration management as foundational pillars for resilient server infrastructure. The absence of community discussions suggests that these were primarily informational updates, without immediate widespread debate or expert commentary within the monitored groups.