Key events and trends
-
Kubernetes Probe Configuration to Prevent Outages: A case study demonstrates how to prevent restarts and deployments from causing outages by separating liveness and readiness probes and properly handling
SIGTERMwith a drain period. (источник)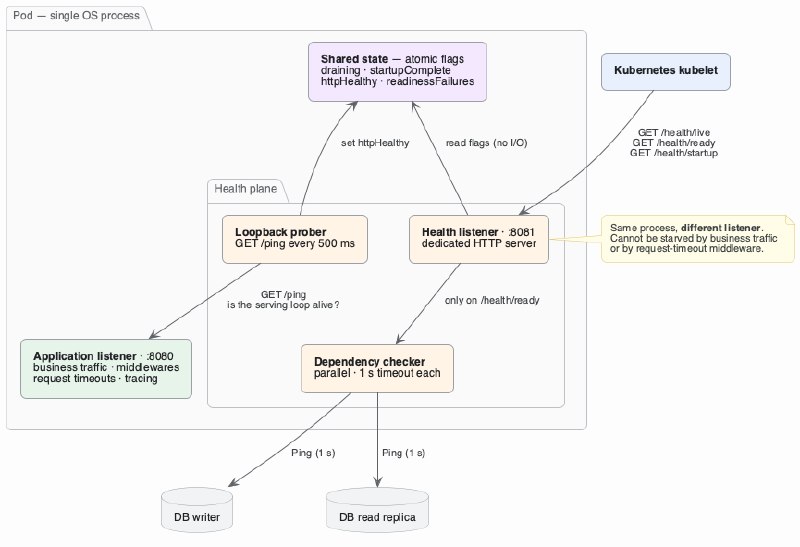
-
Kubernetes as a Tool for Infrastructure Freedom: Yasmin Rajabi, COO at CloudBolt Software, positions Kubernetes as "freedom" for building infrastructure and escaping traditional licensing models and vendor lock-in. She highlights its open-source nature and deployment simplicity, while acknowledging management complexity at scale. (источник)
-
Bitnami Engineering Team Laid Off: The engineering team behind Bitnami, known for hundreds of public container images and Helm charts, has been laid off following Broadcom's acquisition of VMware and subsequent corporate restructuring. This event impacts the availability and maintenance of crucial community-driven infrastructure components. (источник)
-
New Kubernetes Certifications Announced: During KubeCon 2026 NA, two new AI-related Kubernetes certifications, Kubernetes AI Associate (KAIA) and Certified Kubernetes Inference Engineer (CKIE), were announced as being in development. Additionally, the Certified Kubernetes Network Engineer Certification (CKNE), announced a year prior, is now generally available. (источник)
-
Guide to Resizing StatefulSet Persistent Volumes Without Downtime: A practical guide provides methods for resizing persistent volumes for Kubernetes StatefulSets, aiming to achieve this without downtime, though noting potential exceptions based on specific application configurations and environments. (источник)
-
Enforcing Observability with OPA in CI to Prevent Outages: A case study reveals how a 47-minute outage prompted a team to block merges in CI with an Open Policy Agent (OPA) policy, rejecting any service without proper observability settings to enhance infrastructure reliability. (источник)
-
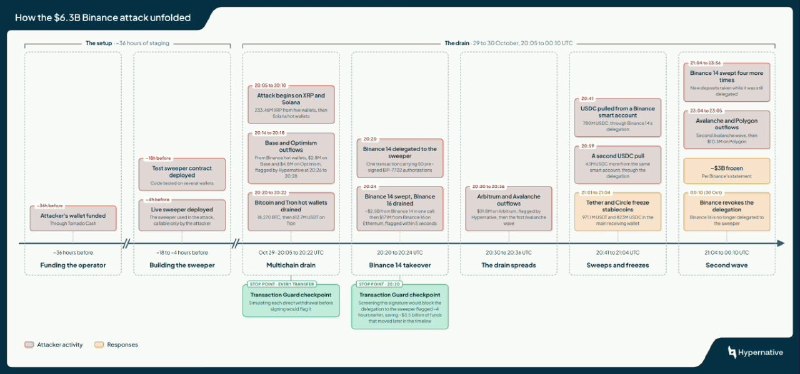
Binance Suffers $6.3B Hot Wallet Drain: On October 29, 2026, attackers drained approximately $6.3 billion from Binance's hot wallets, marking the largest crypto theft on record. The incident was attributed to a compromise of Binance's internal signing keys rather than a smart contract flaw, highlighting critical infrastructure security vulnerabilities. (источник)
-
Postman's Experience Scaling Security Reviews: Postman transitioned their security review process to a risk-based, automation-first model (Security Review v2) to prevent information security from becoming a bottleneck. This involved earlier AppSec team involvement, centralization of security-related information, and adaptable approaches based on service and release criticality, leading to reduced release times and optimized AppSec efforts. (источник)
-
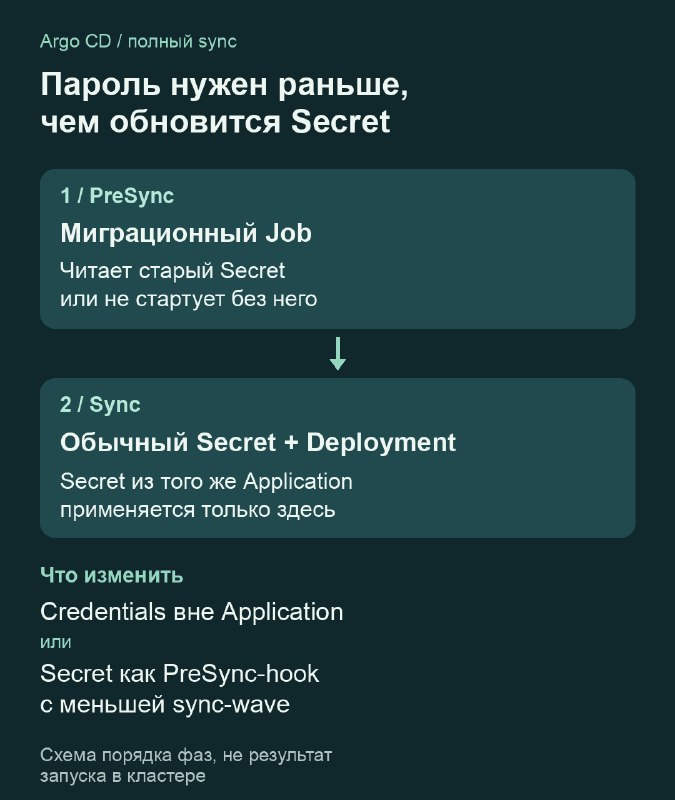
Argo CD PreSync Migration Best Practices: When performing full synchronization in Argo CD, PreSync migration scripts must be idempotent to handle reruns safely. It is also important to manage secrets carefully, as PreSync runs before regular Secrets are available. Verification of migration results needs to be handled externally, as a successful Job only confirms hook completion, not the desired state of an external database. PreSync hooks do not run with selective sync. (источник)
Live discussions
No significant live discussions relevant to server infrastructure and its security were identified during this period.
Social graph
No named participants engaged in relevant discussions during this period.
Final analytics
The day's events highlight a strong focus on enhancing the resilience, security, and operational efficiency of server infrastructure within the Kubernetes and DevOps ecosystem. Key themes include practical guides for maintaining high availability (Kubernetes probes, StatefulSet PV resizing) and advanced deployment strategies (Argo CD PreSync migrations). These underscore the community's drive towards robust, fault-tolerant systems.
Security remains a paramount concern, as evidenced by the large-scale Binance hot wallet drain, which serves as a stark reminder of the critical importance of secure key management and infrastructure protection. Simultaneously, insights from Postman and the case study on OPA policies demonstrate a proactive shift towards integrating security earlier and more deeply into the development lifecycle through DevSecOps practices and automated policy enforcement in CI.
The layoffs at Bitnami signal potential shifts in the open-source ecosystem, particularly concerning the maintenance of widely used container images and Helm charts. This could lead to discussions about community contributions, alternative sources, or potential new initiatives to fill the gap, impacting how development teams consume and manage their dependencies. Overall, the day's content reflects an industry continually adapting to improve system stability, strengthen security postures, and navigate the evolving landscape of cloud-native infrastructure.