Key events and trends
● SKA OCI Daemon Enhances Container Efficiency: The SKA OCI Daemon has been released, designed to optimize OCI registries and compute nodes by improving caching mechanisms and supporting multiple authentication methods. This advancement aims to significantly reduce image pull times for Kubernetes deployments. 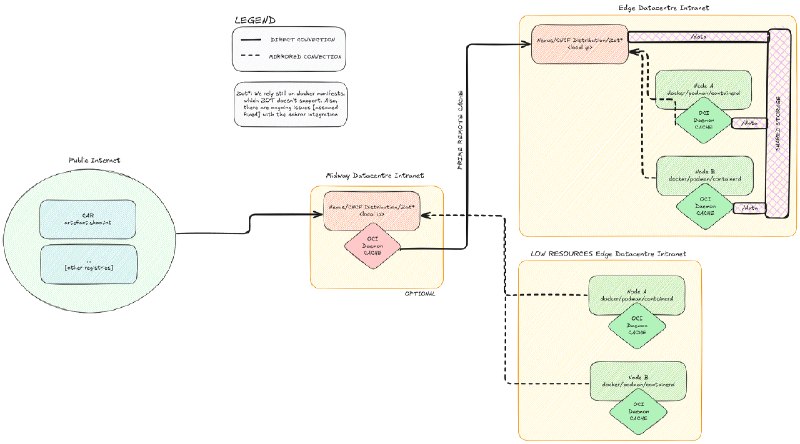 (source)
↳ Community pulse: Members discussed the implications of this release, highlighting its potential to streamline CI/CD processes. @Kubesploit noted its importance in reducing downtime during deployments.
● Critical Brotli Decoder Vulnerability (CVE-2026-111497): A critical vulnerability has been identified in the Brotli decoder, which can allow remote code execution. This flaw necessitates immediate attention from developers using affected libraries. More details can be found in the linked blog post.  (source)
↳ Community pulse: @devsecops_weekly emphasized the need for proactive vulnerability management, urging developers to assess their applications for this vulnerability.
● ArgoCD Bottleneck Resolution: An article shared by @CatOps details how a colleague resolved a bottleneck in ArgoCD caused by an inefficient Kubernetes API call. The fix involved using informers to improve resource fetching efficiency. This serves as a cautionary tale for developers in the Kubernetes ecosystem. (source)
↳ Community pulse: @Kubesploit pointed out that understanding such bottlenecks is crucial for maintaining high performance in CI/CD pipelines, sparking a discussion on best practices for optimizing Kubernetes controllers.
Live discussions
- Handling Secrets in Container Images: A discussion emerged around the risks of accidentally embedding secrets within Docker images. @devsecops_weekly highlighted a scenario where a secret could be retrievable even after deletion, stressing the importance of secure handling practices. The conversation included recommendations for managing secrets effectively during image creation.
Social graph:
- @Kubesploit: Expert on Kubernetes practices, contributed to discussions on the SKA OCI Daemon and ArgoCD.
- @devsecops_weekly: Initiator of the discussion about vulnerabilities and secret management in container images.
- @CatOps: Shared insights on ArgoCD and highlighted the importance of understanding bottlenecks.
Final analytics:
Today's discussions focused heavily on security and performance improvements within the Kubernetes ecosystem. The release of the SKA OCI Daemon represents a significant step towards optimizing container management, while the critical Brotli vulnerability underscores the ongoing challenges of maintaining security in modern applications. The community's proactive approach to discussing best practices for secret management reflects a growing awareness of security risks associated with containerization. However, gaps remain regarding comprehensive strategies for vulnerability management, indicating a potential area for further exploration and education within the community. Overall, the tone was constructive, with members eager to share insights and solutions.