Key events and trends
● New Game "chaossnake" Deletes Kubernetes Pods: A terminal game, "chaossnake," allows players to delete real Kubernetes pods while playing Snake. Each food item represents a pod, and moving triggers a kubectl delete command. (source)
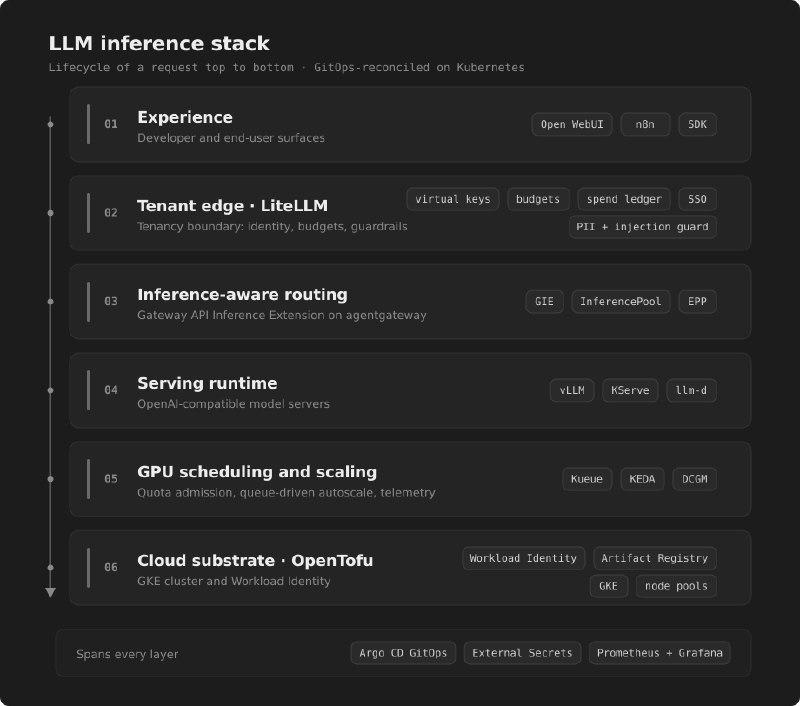
● vLLM in Kubernetes Pods: An article discusses the necessity of additional layers around vLLM in Kubernetes pods, including tenant keys, inference-aware routing, and GPU scheduling, to create a functional LLM platform. (source)
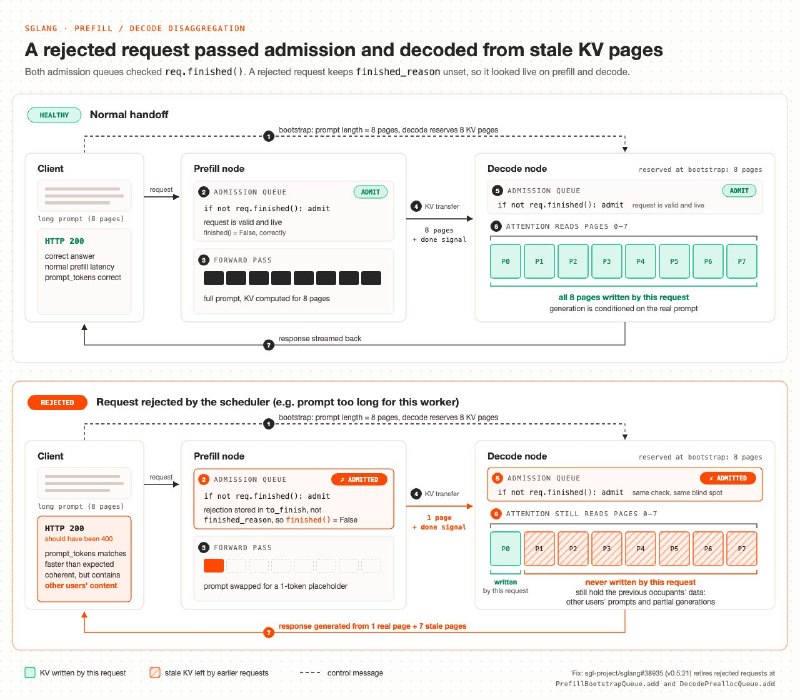
● Cloudflare Remediates GLM-5.3 KV Cache Exposure: A configuration mismatch in the GLM 5.3 Workers AI model led to an SGLang bug exposing KV cache pages. Cloudflare's remediation process is detailed in their blog. (source)
Live discussions
- Secret Management Challenges: @devsecops_weekly initiated a discussion on managing secrets without breaking existing systems. They highlighted the complexities of ensuring visibility and ownership of secrets, emphasizing that simply implementing Vault is not sufficient. The conversation explored various nuances, such as the differences between secrets and tokens, and the need for a systematic approach to secret management.
Social graph
- @devsecops_weekly: Initiator of the discussion on secret management.
- @cloud_sec: Contributor discussing the KV cache exposure incident.
- @LearnKubeNews: Shared insights on the new game and LLM platform requirements.
Final analytics
Today's discussions highlighted significant developments in Kubernetes and DevOps, particularly concerning security and infrastructure management. The introduction of "chaossnake" adds a unique layer to how Kubernetes can be interacted with, while the article on vLLM emphasizes the complexities of implementing advanced AI solutions in Kubernetes environments.
The Cloudflare incident serves as a reminder of the ongoing vulnerabilities in cloud infrastructure, underscoring the importance of robust security measures. The dialogue around secret management reflects a growing awareness of the intricacies involved in securing sensitive data within Kubernetes, indicating a shift towards more comprehensive governance practices.
Overall, the tone of the discussions was constructive, with a focus on problem-solving and knowledge-sharing. However, gaps remain in understanding best practices for secret management, suggesting that further exploration and community engagement will be necessary to address these challenges effectively.