Key events and trends:
● Optimizing Observability Costs in NGINX-to-Envoy Migrations: Migrating proxies from NGINX to Envoy without validating telemetry can significantly increase observability costs due to extreme volume and cardinality of metrics. Henrik Rexed recommends treating observability configuration as software and validating it during development with tools like OpenTelemetry Weaver before production deployment (источник).
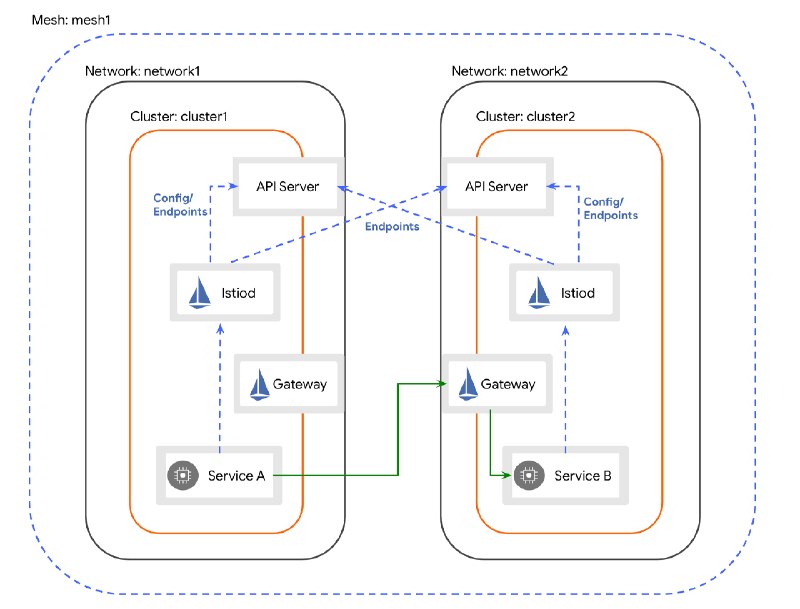
● Multi-Cluster Amazon EKS with Istio and Kiali: A new tutorial demonstrates how to connect two Amazon EKS clusters using an Istio multi-primary, multi-network mesh, allowing for centralized monitoring and visualization through Kiali (источник).
● KubeVirt and NATS Achieve CNCF Graduated Status: KubeVirt, a virtual machine management add-on for Kubernetes, and NATS, a high-performance cloud- and edge-native messaging system, have officially graduated to CNCF status. KubeVirt was accepted in 2019 and incubated in 2022, with adopters including Microsoft and Red Hat. NATS, accepted in 2018, saw a dispute over ownership last year but remains with CNCF, with notable adopters like Mastercard and Walmart (источник).
● Leveraging a Security Constitution for Cloud Flaw Detection: A "Security Constitution" comprising 12 principles, 11 lessons, and 13 trust anchors has been used to guide an LLM harness in identifying insecure-by-design cloud flaws, specifically missing controls. This approach led to 109 findings across Google Cloud Platform (GCP) and Azure, with the article detailing five specific cases (источник).
● Addressing Package Manager Integrity Issues: Research into 25 popular package managers revealed significant vulnerabilities in their integrity control mechanisms. Many managers fail to verify the integrity of downloaded packages, even when hash values are present but not utilized for validation, allowing compromised repositories to inject malicious code. This highlights critical supply chain security risks (источник).
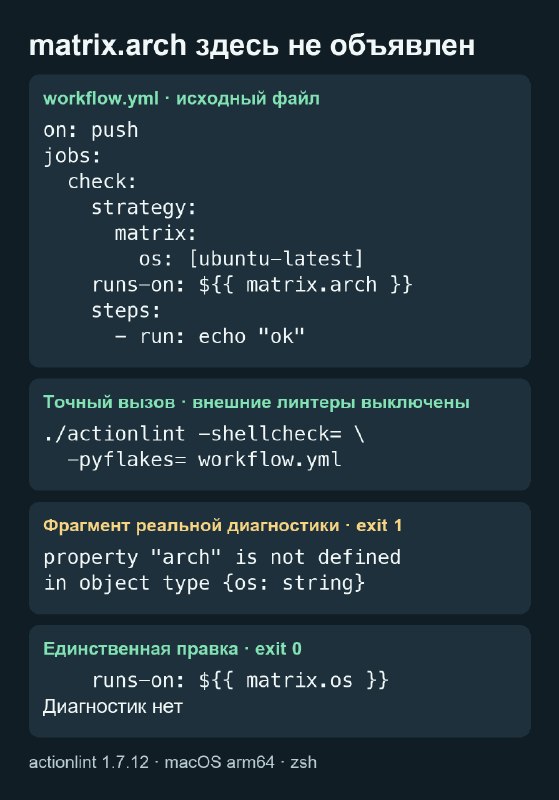
● Pre-CI Workflow Linting with actionlint: The actionlint tool can identify typos in GitHub Actions matrix configurations locally before a Continuous Integration (CI) run, preventing potential issues and improving the reliability of CI/CD workflows (источник).
● AWS Serverless Adoption in 2026: Oleg Pustovit shares insights on building startup backends using AWS Serverless services like Lambda, SQS, and DynamoDB. The discussion compares AWS serverless with alternatives such as Vercel and Cloudflare, providing practical use cases and outlining when serverless is the optimal choice and when other approaches are preferable (источник).
● Friday Security Humor: A video related to security was shared to mark Friday (источник).
 Watch video
Live discussions:
No relevant live discussions were recorded for this period.
Social graph:
- @LearnKubeNews: Posted on observability costs and EKS multi-cluster setup.
- @kubernative: Reported on CNCF project graduations.
- @devops_sre_notes: Shared a security-themed humorous video.
- @cloud_sec: Published an article on cloud security flaw detection using a "Security Constitution."
- @devsecops_weekly: Provided an analysis of package manager integrity issues.
- @devopsslib: Highlighted the utility of
actionlintfor CI/CD workflow linting. - @devops_dou: Shared insights on AWS serverless adoption.
Final analytics:
The day's content strongly emphasized server infrastructure, cloud security, and DevOps best practices. A recurring theme was the focus on validation and integrity: validating telemetry configurations to manage observability costs, ensuring the integrity of package managers to mitigate supply chain risks, and pre-checking CI/CD workflows for errors. The graduation of KubeVirt and NATS highlights continued growth and maturity within the Kubernetes ecosystem, extending its capabilities to virtual machine management and high-performance messaging. Cloud security remains a critical area, with innovative approaches like using an "AI Security Constitution" to identify architectural flaws in cloud environments. Overall, the tone was informative and practical, focusing on tools, methodologies, and architectural considerations crucial for maintaining secure and efficient server infrastructure. No significant information gaps were observed, and discussions leaned towards problem-solving and strategic decision-making in cloud-native environments.